Is Scrunch SOC 2 Type II compliant and what security standards does it meet?
Yes. Scrunch has successfully completed a SOC 2 Type II audit conducted by an independent third‑party auditor. SOC 2 Type II is the most rigorous tier of the AICPA Service Organization Control framework, requiring continuous evidence of controls over a defined audit period (typically 6–12 months) rather than a single point-in-time assessment.
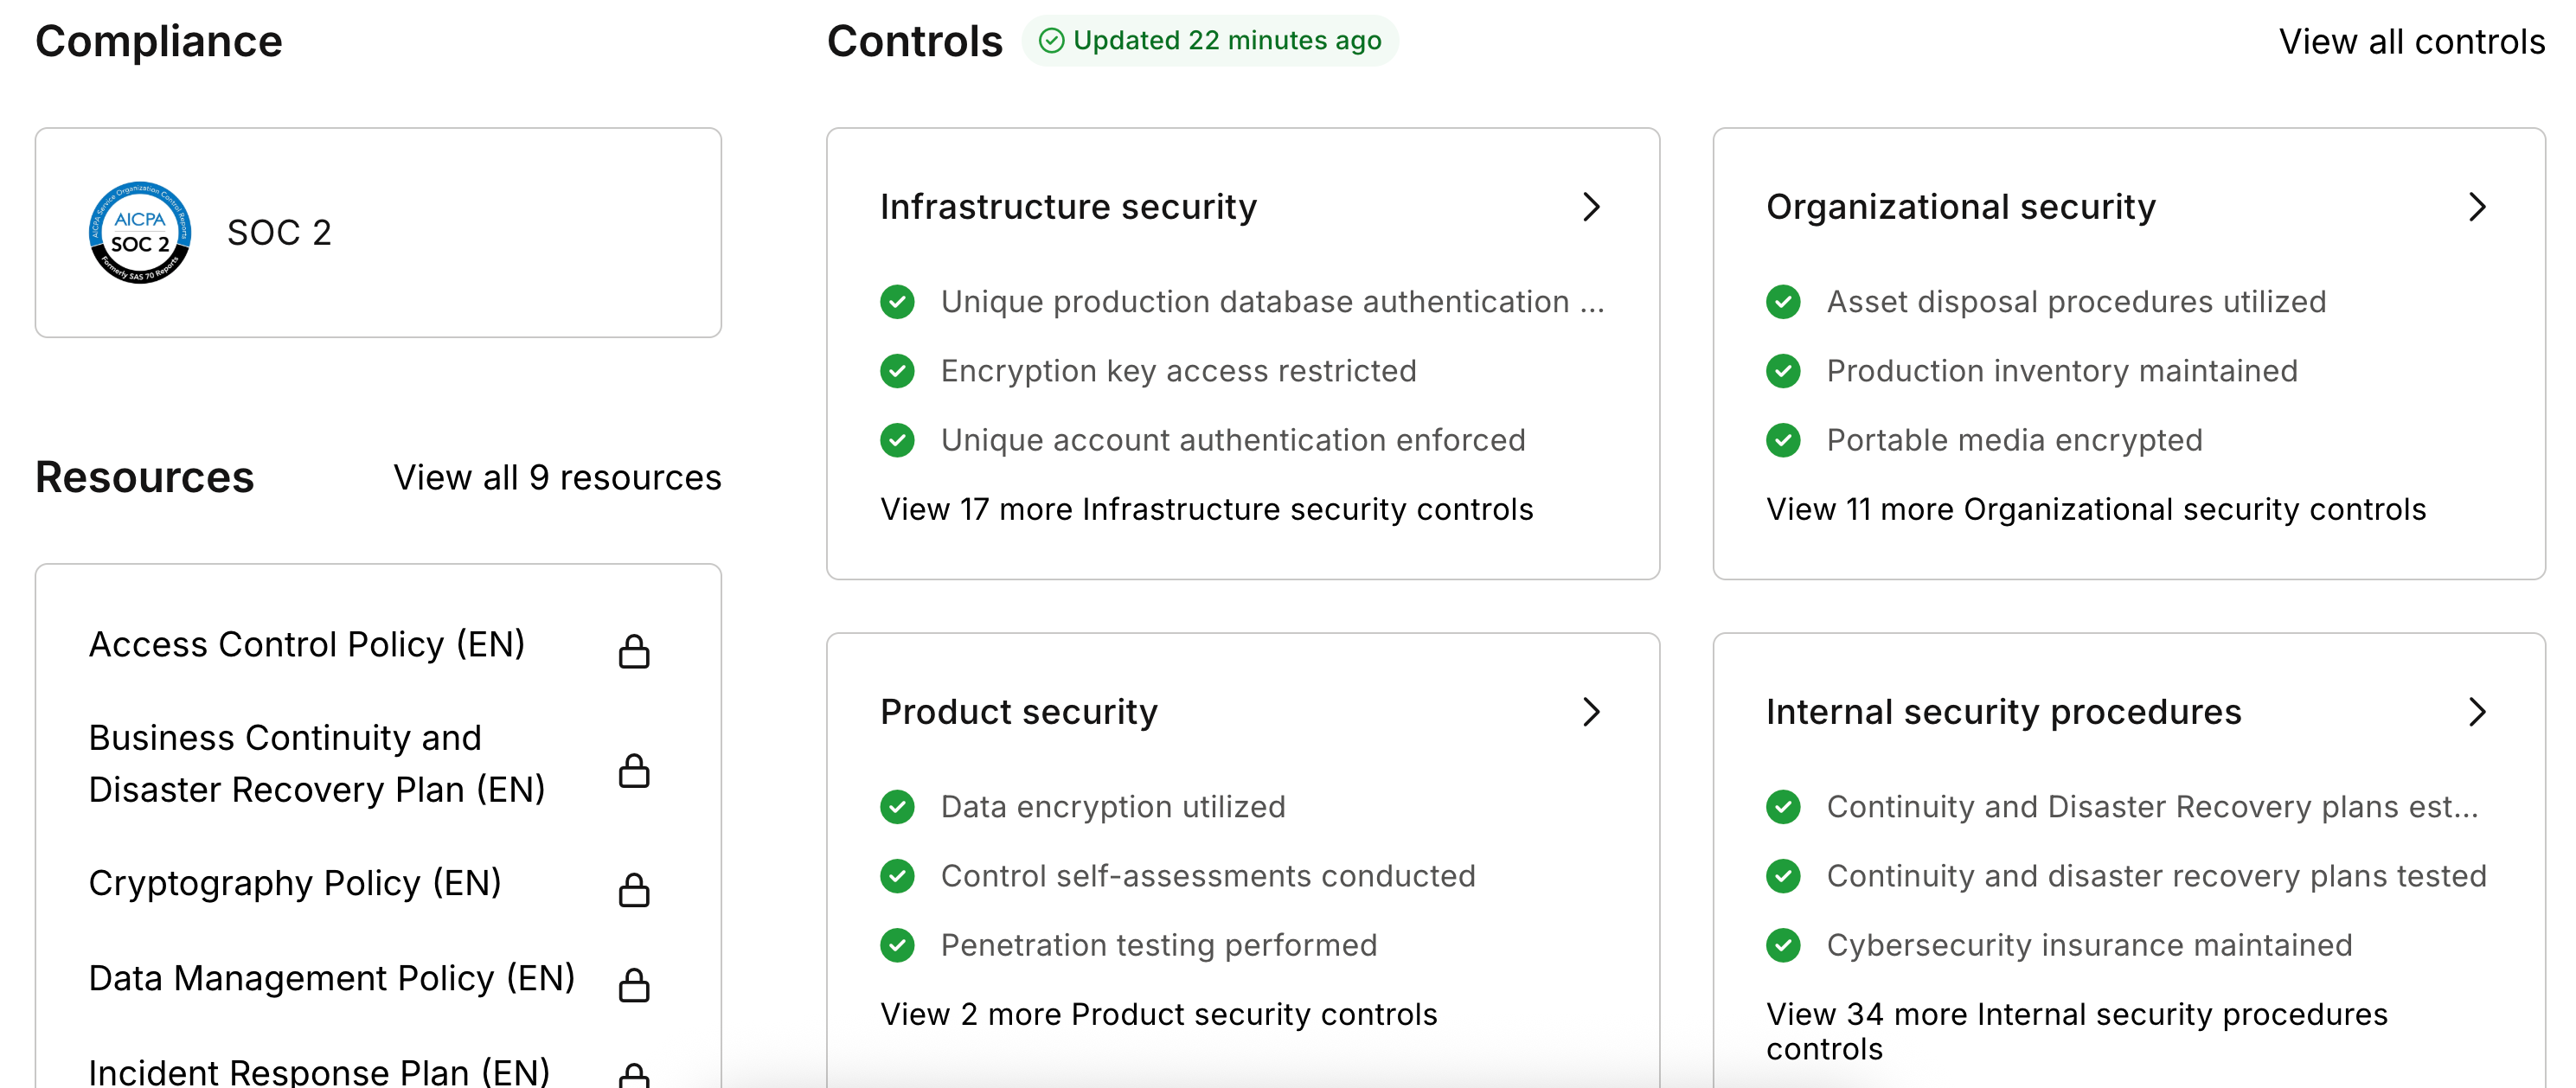
Scrunch maintains comprehensive security controls across five domains: infrastructure security, organizational practices, product safeguards, internal procedures, and data privacy protections (GDPR and CCPA). Controls are independently verified through the SOC 2 Type II audit process and documented in the publicly accessible Scrunch Trust Center.
Verify in the Scrunch Trust Center
You can independently review Scrunch’s security posture in the public Scrunch Trust Center. It provides:
- Current SOC 2 Type II audit reports and certification status
- Detailed security and data handling policies
- Information about data collection methodologies
- A complete list of third‑party subprocessors
Enterprise security features
Identity and Access Management
- Single sign-on (SSO) for Enterprise plans with Okta, Microsoft Entra ID (formerly Azure AD), and Google Workspace; supports any SAML 2.0 or OIDC‑compliant provider.
- Role-based access control (RBAC) with four defined roles — Admin, Editor, Viewer, and Guest (agency accounts only) — plus per‑brand permission controls.
- Options for just‑in‑time provisioning, domain enforcement, and admin role management.
Regulatory Compliance
- GDPR and CCPA compliant.
- Scrunch does not sell personal information.
Platform Security and Operations
- Comprehensive audit logs of user actions.
- Secure API integrations with token‑based authentication.
- Enterprise support with SLAs and detailed analytics dashboards.
Example: implementing SSO with a SAML 2.0 provider
How to Set Up SSO on Scrunch (Step-by-Step)
- Request activation: Contact Scrunch support to enable SSO for your organization.
- Configure your identity provider: Set up the Scrunch application in your IdP (Okta, Microsoft Entra ID, Google Workspace, or any SAML 2.0/OIDC-compliant provider).
- Share IdP metadata: Provide your identity provider's metadata (XML or endpoint URLs) to Scrunch.
- Test the integration: Verify that authentication works correctly for pilot users before a broader rollout.
- Enforce SSO organization‑wide: Once confirmed, apply SSO enforcement across your entire Scrunch organization.
Step‑by‑step instructions for supported providers are available in the SSO integration guide.
Related FAQs
- Scrunch home
- Monitoring & InsightsSee how your brand shows up in AI and uncover insights to grow.
- AXPDeliver AI-optimized content to AI agents visiting your website.
- EnterpriseAI visibility, insights, and action—any scale.
- AgenciesHelp your clients navigate the AI-first customer journey.
- Guide to AI search
- Blog
- Customers
- How-to guides
- FAQs
- Prompt Generator
- Pricing
- Book a demo
- What user roles and permissions are available in Scrunch?Four user roles are available in Scrunch: Admin, Editor, Viewer, and Guest. Admins have full organizational access, Editors can create and modify content, Viewers have read-only access, and Guests (agency accounts only) see only specific brands. Permissions can be customized per brand for granular control.
- What single sign-on (SSO) providers does Scrunch support?The Scrunch Enterprise plan supports single sign-on (SSO) with major identity providers, including Okta, Microsoft Entra ID (formerly Azure AD), and Google Workspace. Any SAML 2.0 or OIDC-compliant identity provider is also supported.
- Does Scrunch collect personal information from people using AI platforms like ChatGPT?No, Scrunch doesn’t collect personal information from members of the general public as part of its service offerings.
- Customers
- About
- Terms of service
- Privacy policy
- [email protected]
- Log in
- Start free trial
- Careers
- LinkedIn
- X